Compliance that operates continuously.
Investigations produce records. Compliance Operations turns those records into a defensible, continuously improving privacy program: corrective actions tracked, policies reviewed, leadership informed, and OCR documentation organized as part of how the program runs every day.
Most healthcare organizations are compliant in practice. The problem is demonstrating it.
Individual cases may be handled well. But when OCR asks for evidence of a consistent privacy program, or when the board asks for a governance summary, the answer often requires assembling documentation that doesn’t exist in one place.
“We had the investigations. We had the evidence. What we didn’t have was a way to show, consistently and quickly, that we had a program, not just a stack of case files.”
Composite perspective · Healthcare Chief Privacy Officer
What happens to investigation records at the program level
Closing an investigation is the beginning of the program management cycle, where case data becomes policy guidance, corrective action, and leadership reporting.
The operational view your privacy program leadership actually needs
The Compliance Operations workspace is designed for the Chief Privacy Officer and Compliance Officer, not for individual case management, but for program oversight.
Every open action, visible
Patterns across cases
What requires attention next
Illustrative interface · all data drawn from actual investigation and corrective action activity
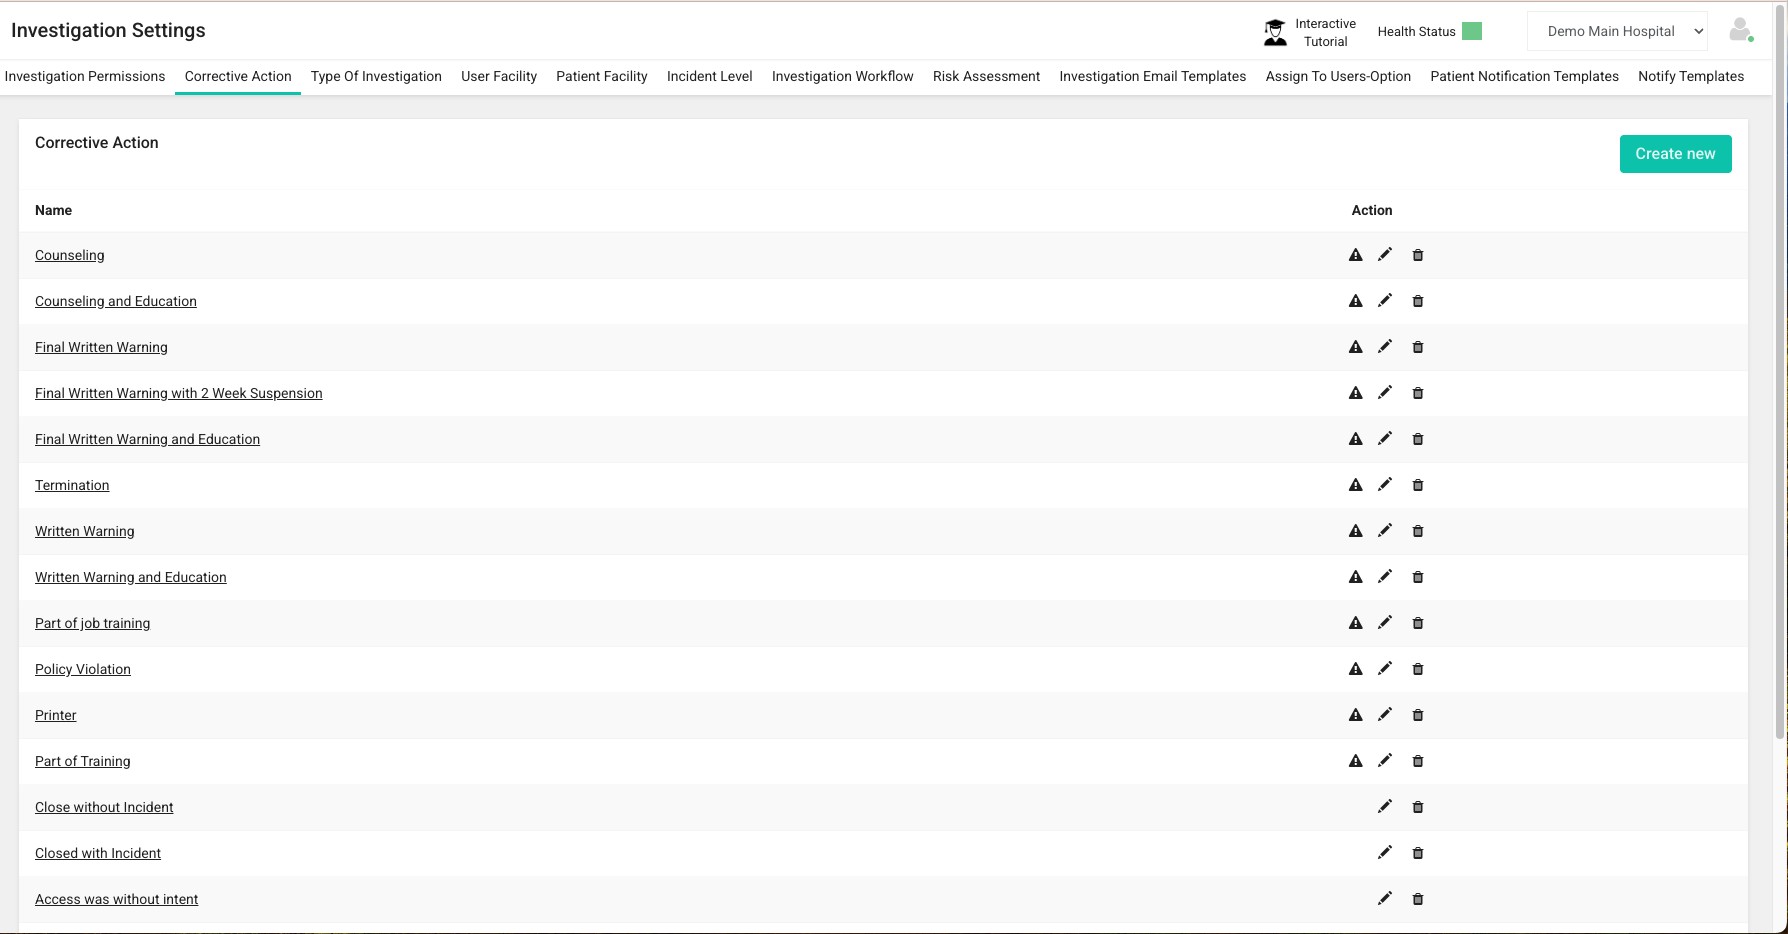
Your corrective actions, your terminology
Admins define the corrective actions available when a case closes, such as counseling, a written warning, or termination, and can add, edit, or retire them without a support ticket.
Built for the operational demands of a mature privacy program
Each capability addresses a specific gap in how healthcare organizations manage privacy compliance at the program level, above the individual investigation, across the full program.
Corrective action tracking
Keep every corrective action visible, accountable, and on schedule. Education requirements, policy acknowledgments, supervisor follow-ups, and disciplinary steps appear in a unified view.
Nothing is forgotten because it was buried in a closed case.Policy management
Connect policy review to what investigations actually reveal. When violation patterns signal a gap, that gap is visible, rather than buried in individual case records.
Policies update when the evidence says they should.OCR audit preparation
When OCR requests documentation, the answer is retrieval, not a preparation project. Investigation records are organized with monitoring evidence, breach risk assessment, corrective action, and disposition.
The preparation is a byproduct of normal operations.Risk trending and program analytics
Surface where risk is concentrating before it becomes a compliance exposure. Investigation data across the full program is aggregated into a program-level view by department, type, and trend direction.
Privacy leadership sees what the data shows before OCR does.Executive reporting
Give CPOs, executives, and the board program performance data drawn from actual activity, not assembled manually before every leadership meeting.
Leadership sees the program, not a curated summary of it.Hotline intake & exclusion screening
A complete compliance program includes confidential workforce intake and exclusion screening against OIG and GSA SAM lists, both feeding the same program record.
Monitoring, investigation, intake, and exclusion in one platform.Evidence repository
Investigation records, corrective action confirmations, policy versions, and breach risk assessments are maintained in a structured, retrievable repository.
The privacy program’s full history is always available for regulatory response or audit.Continuous improvement
The compliance program improves through the data it generates: investigation patterns drive policy review, corrective action outcomes reveal whether training is working, department trends point to where intervention is needed next.
The privacy program gets stronger because it learns from its own history.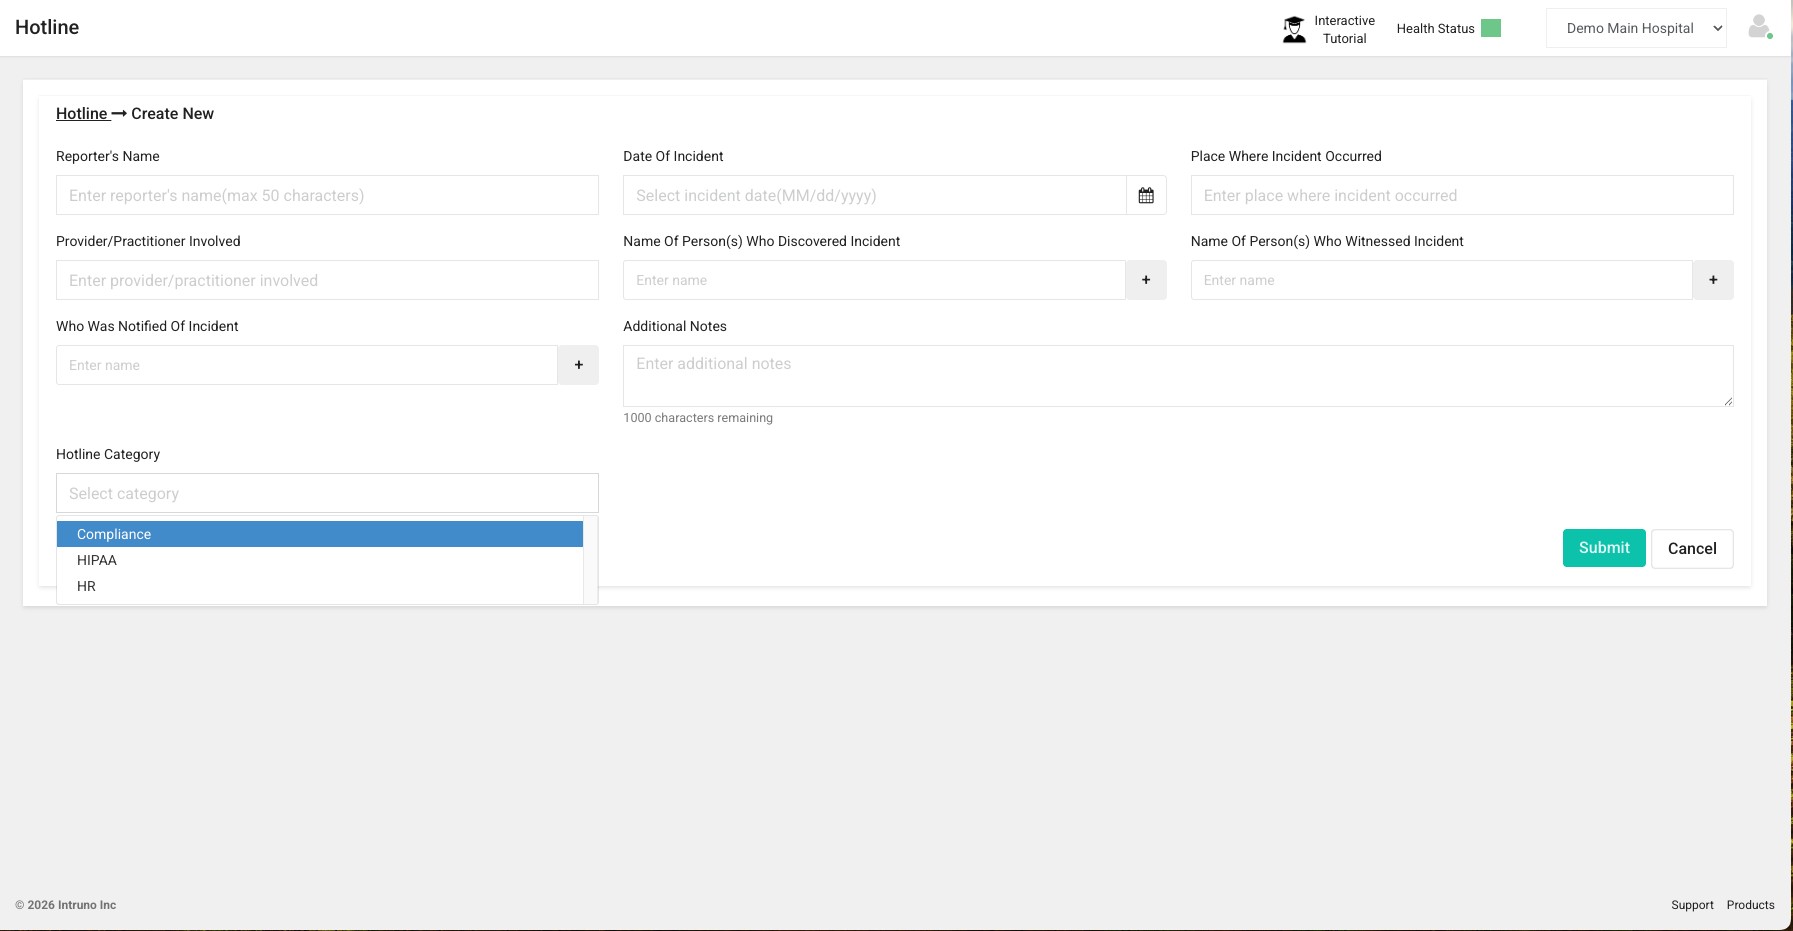
Structured hotline intake
Each report captures the reporter, the date and place of the incident, the provider involved, and who discovered or witnessed it. Reports are categorized as Compliance, HIPAA, or HR at intake so they reach the right reviewer.
Every role in the privacy program needs different information
The same underlying data serves five different reporting audiences, but what each receives should reflect their role, not a one-size-fits-all summary.
All views generated from the same underlying investigation and corrective action data: no manual preparation at any level.
A privacy program that learns from its own data
The purpose of a compliance program is not to document violations. It is to reduce them. That requires learning from investigation patterns, corrective action outcomes, and trends that tell you where the program has gaps before regulators find them.
Organizations that treat compliance as an annual exercise find themselves permanently reactive. Intruno connects the cycles: what the program learns from one investigation can improve how it handles the next one.
Investigation data captured
Every case creates a structured record.
Patterns identified
Aggregate analysis surfaces repeat behaviors and concentrations.
Gap identified
A repeating pattern signals a policy or training gap.
Response targeted
Policy updated or training targeted from evidence.
Behavior monitored
Subsequent cases show whether the intervention worked.
The cycle continues
Each quarter builds on the last.
What mature privacy programs look like
Maturity is a trajectory from reactive response to continuous, evidence-based improvement, earned through the accumulation of operational intelligence and the discipline to act on it.
Reactive
Investigations triggered by complaints or audits. No systematic monitoring.
Repeatable
Investigation process exists but is inconsistent. Documentation varies.
Managed
Investigations follow a defined process. Evidence captured. Corrective actions tracked.
Measured
Program data visible across time. Trends tracked. Department concentrations surfaced. Leadership receives intelligence.
Continuously improving
Investigation data drives policy, training, and resource decisions. Program maturity is demonstrable.
Where does your program sit today?
What continuous compliance operations change at an organizational level
The improvements described on this page represent a structural shift in how a healthcare organization demonstrates, manages, and improves its privacy compliance posture.
Always audit ready
When every investigation is structured and every corrective action is tracked continuously, audit readiness is simply the current state of the program.
When the inquiry arrives, the answer is retrieval, not a documentation project.Dramatically reduced preparation effort
Hours spent preparing for audits, assembling executive reports, and tracking corrective actions across systems return to investigation quality and program improvement.
Preparation effort becomes a continuous byproduct of normal operations.Executive visibility without manual effort
CPOs and executives have access to program performance data generated from actual investigation activity, without requiring a report before each leadership meeting.
Leadership sees the program, not a summary of it, and the data is current.Measurable privacy program maturity
Program maturity is a trajectory visible in longitudinal data: repeat violations, corrective action completion, and case closure trends over time.
The answer to “is our program getting stronger?” is in the data.Stronger governance and accountability
Every corrective action is assigned, tracked, and confirmed. Every policy review is documented. Every escalation leaves a record. Governance is structural.
Accountability is built into how the program operates, not asserted after the fact.Reduced operational risk over time
As the program improves from its own data (policies updated from case patterns, training targeted by evidence) the underlying violation rate can trend toward reduction.
The best defense against future OCR exposure is a program that demonstrably improved because of how it handled past violations.See what a continuously operating privacy program looks like
A 30-minute conversation with the Intruno team, focused on your current compliance operations, your leadership reporting needs, and where your program most needs to mature.