One platform for the complete healthcare privacy lifecycle.
Monitoring, behavioral intelligence, investigation, and reporting share one system of record, so nothing gets re-explained as a case moves from a flagged event to a resolved, documented outcome.
Request a DemoHow the work connects
Six areas of work, linked by shared workflows rather than a single fixed sequence. Click one to see how it fits.
Continuous visibility into patient-data access across every system, capturing who viewed what, when, and under what role.
Six capabilities, one shared context.
Continuous visibility into who accesses what, when, and why it matters.
Every access event carries context: role, relationship to the patient, timing, and location, instead of arriving as a bare log line.
Learn more →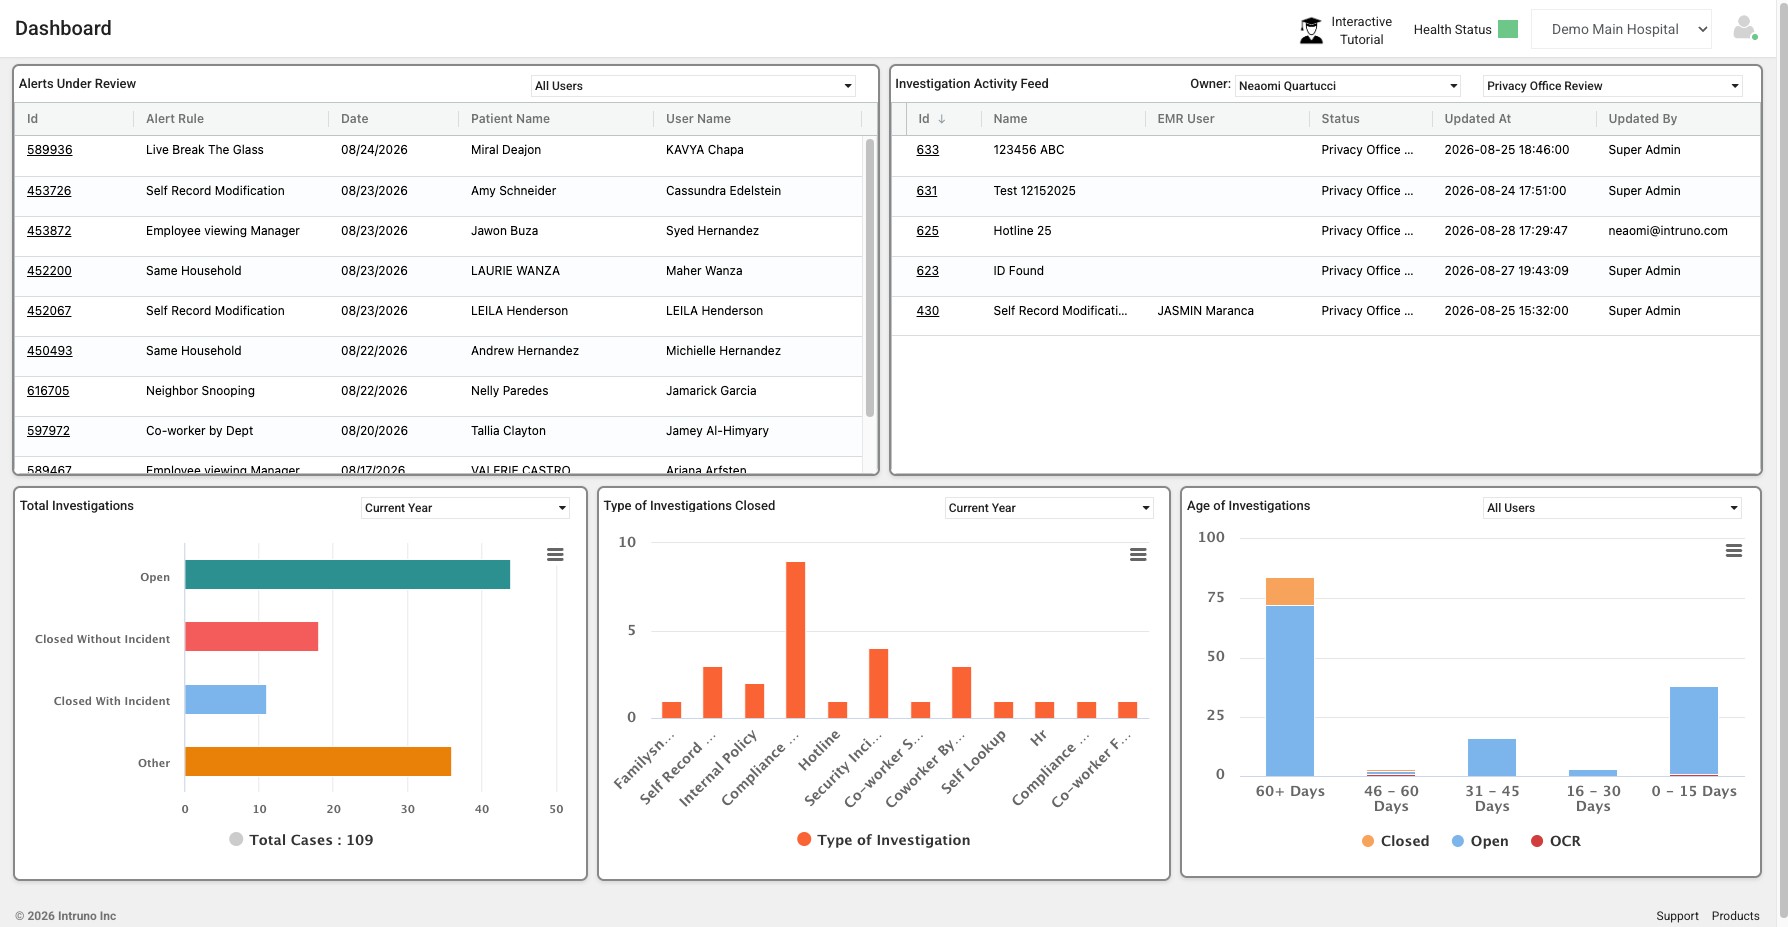
Patterns across time, not single events in isolation.
Intruno looks at behavior in context: how it compares to a person’s normal pattern and their peers in similar roles, to surface what actually warrants attention.
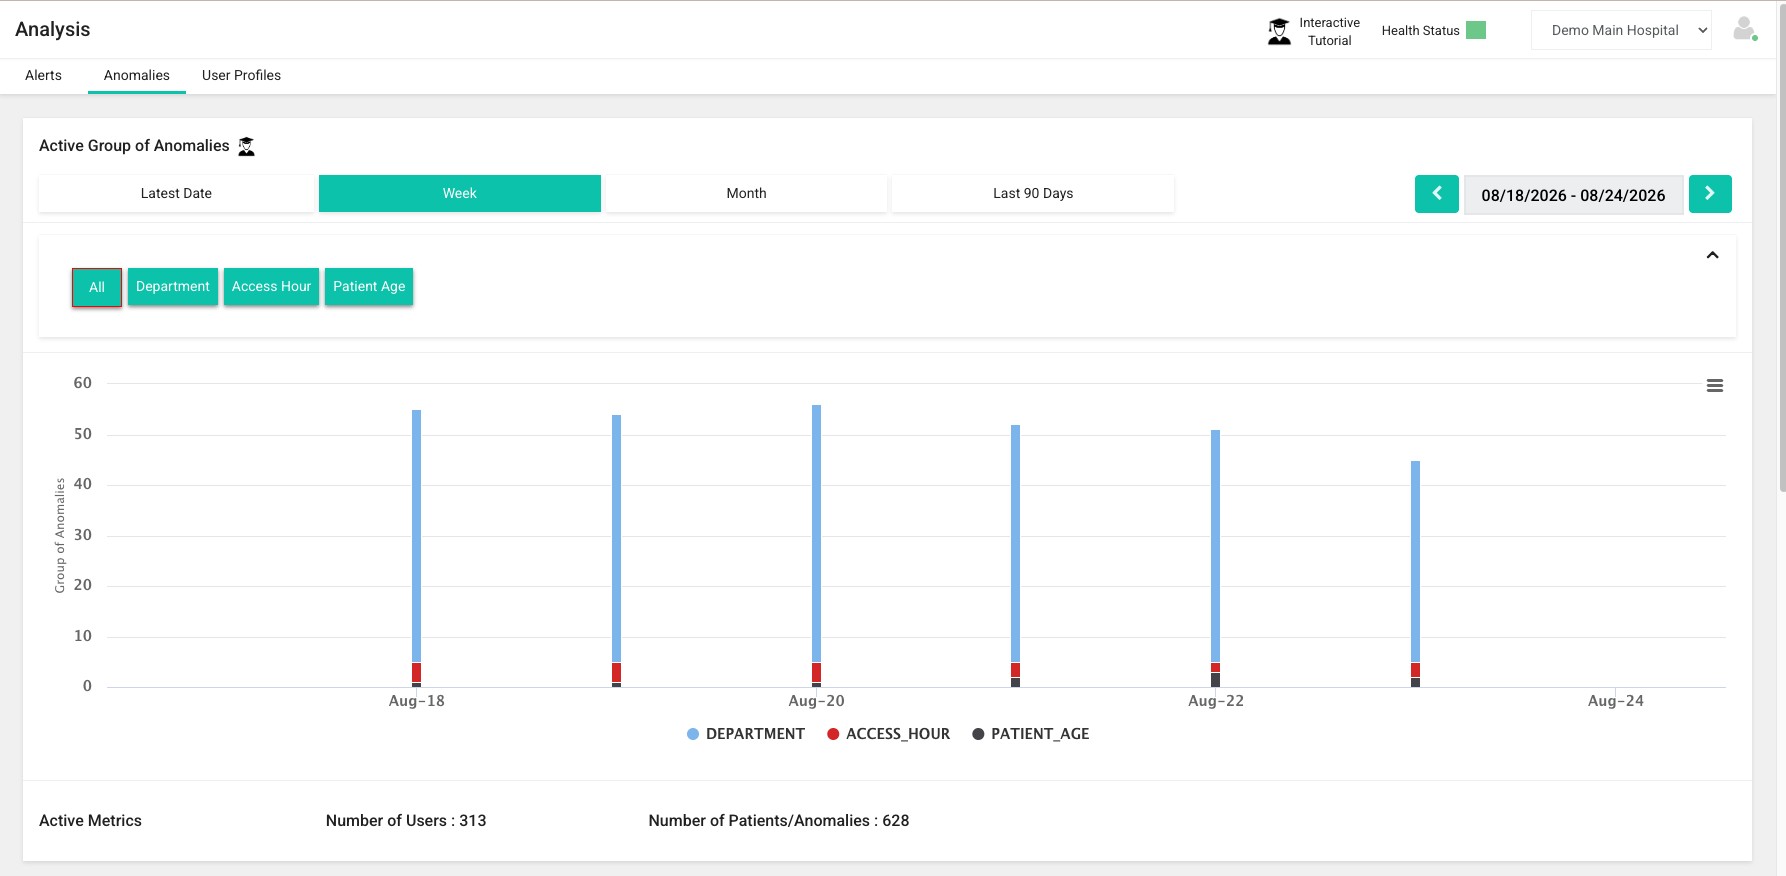
Alerts prioritized by relevance, not just volume.
Rather than a flood of undifferentiated events, alerts are grouped by the person, the pattern, and the potential impact, so review time goes where it matters.
A structured path from alert to documented decision.
Investigators work from an assembled case file: evidence, notes, and prior context together, rather than reconstructing it across systems.
See the investigation experience →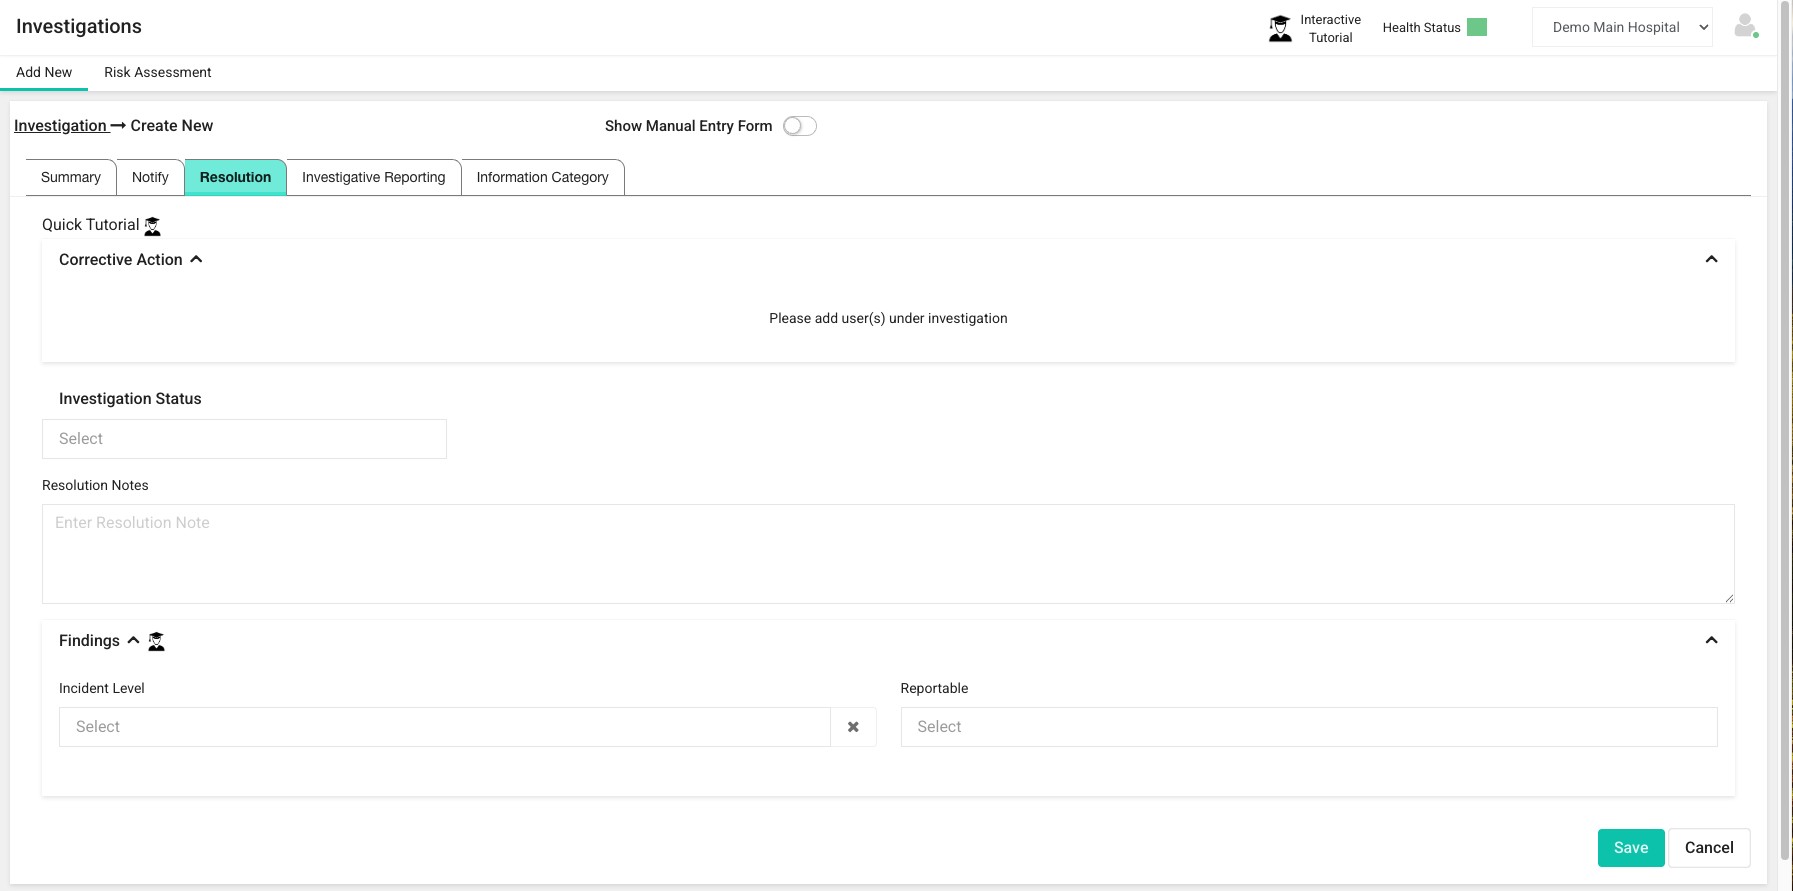
Evidence and outcomes, organized for audit from day one.
Case history, decisions, and resolutions are documented as they happen, so compliance teams aren’t reconstructing a paper trail after the fact.
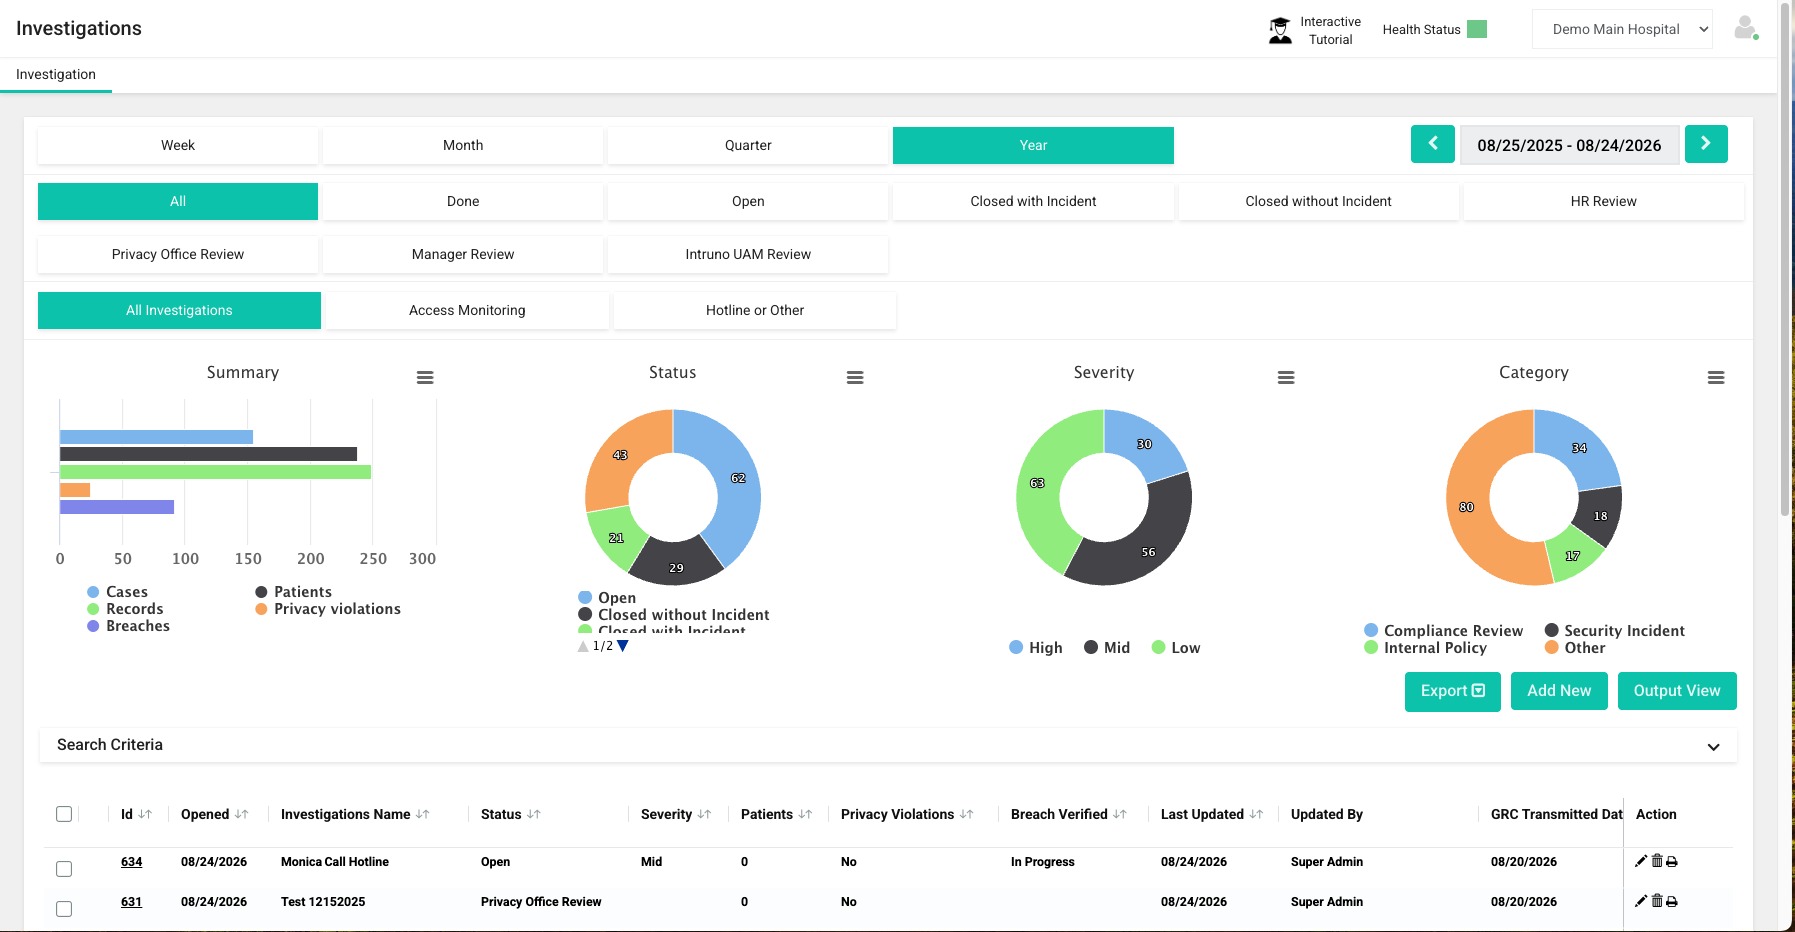
The same intelligence, applied to conversations and calls.
Hotline Nate transcribes conversations, captures notes, and understands context, applying stakeholder tags for the teams involved on the healthcare organization’s side, such as Privacy, Compliance, Security, IT, or HR, so the right context reaches the right case.
Conceptual preview: capabilities shown here represent product direction, not a finalized feature.
Request a demo →From the first access event to the final compliance report
In most privacy programs, monitoring, investigation, and compliance reporting are three separate efforts. In Intruno, they’re one continuous workflow, each stage handing off to the next automatically.
Every access event, continuously ingested
Intruno connects to your EHR systems and ingests access events in real time. It builds a behavioral baseline for each user, factoring in role, care responsibilities, and typical access patterns, so what counts as “normal” is specific to them, not averaged across a department.
Deviations become findings, not raw flags
When access deviates from baseline, Intruno checks whether a documented care relationship exists before generating an alert. What reaches your team is an actionable finding with clinical context already attached, not a log entry that still requires hours of manual research.
Alert becomes case in one step
One action converts an alert into a formal case. The full context transfers automatically: user profile, access history, patient record, policy triggered. Every subsequent action inside Intruno builds the case record as the work happens.
Dispositions are documented, not ignored
Every case closes with a recorded outcome: the finding, the action taken, who was notified, and the disposition. Cases that escalate to HR, Legal, or a GRC platform carry their full record forward. Nothing is lost between systems.
Compliance documentation builds as you work
Because every action is captured in sequence, reporting is a byproduct of normal workflow, not a separate effort. When OCR requests documentation, the monitoring evidence, investigation records, and remediation proof are already organized.
Investigation data closes the loop into policy
The aggregate record of your investigations, which departments generate repeat violations, which corrective actions hold, feeds directly into program policy decisions. The program improves because the data is in one place.
Alert → Case: one action, no lost context
The moment an alert becomes an investigation is where most programs lose information. In Intruno, this handoff is automatic: every field the analyst would have typed already exists in the case when they open it.
Most platforms stop at detection
Monitoring tools surface violations. Intruno is built around what comes after: the investigation, the resolution, and the audit trail. Detection without a connected investigation system creates a different kind of fragmentation.
Customized workflows with designated ownership and clear handoffs
Each module covers a distinct operational domain. Here’s what it does, who uses it, and where it connects to the rest of the platform.
Patient Privacy Monitoring
The detection layer. Connects to your EHR and builds a behavioral baseline for every user. When access deviates, care relationship validation runs before any alert is generated. What reaches your team is a real finding with clinical context attached.
Investigations
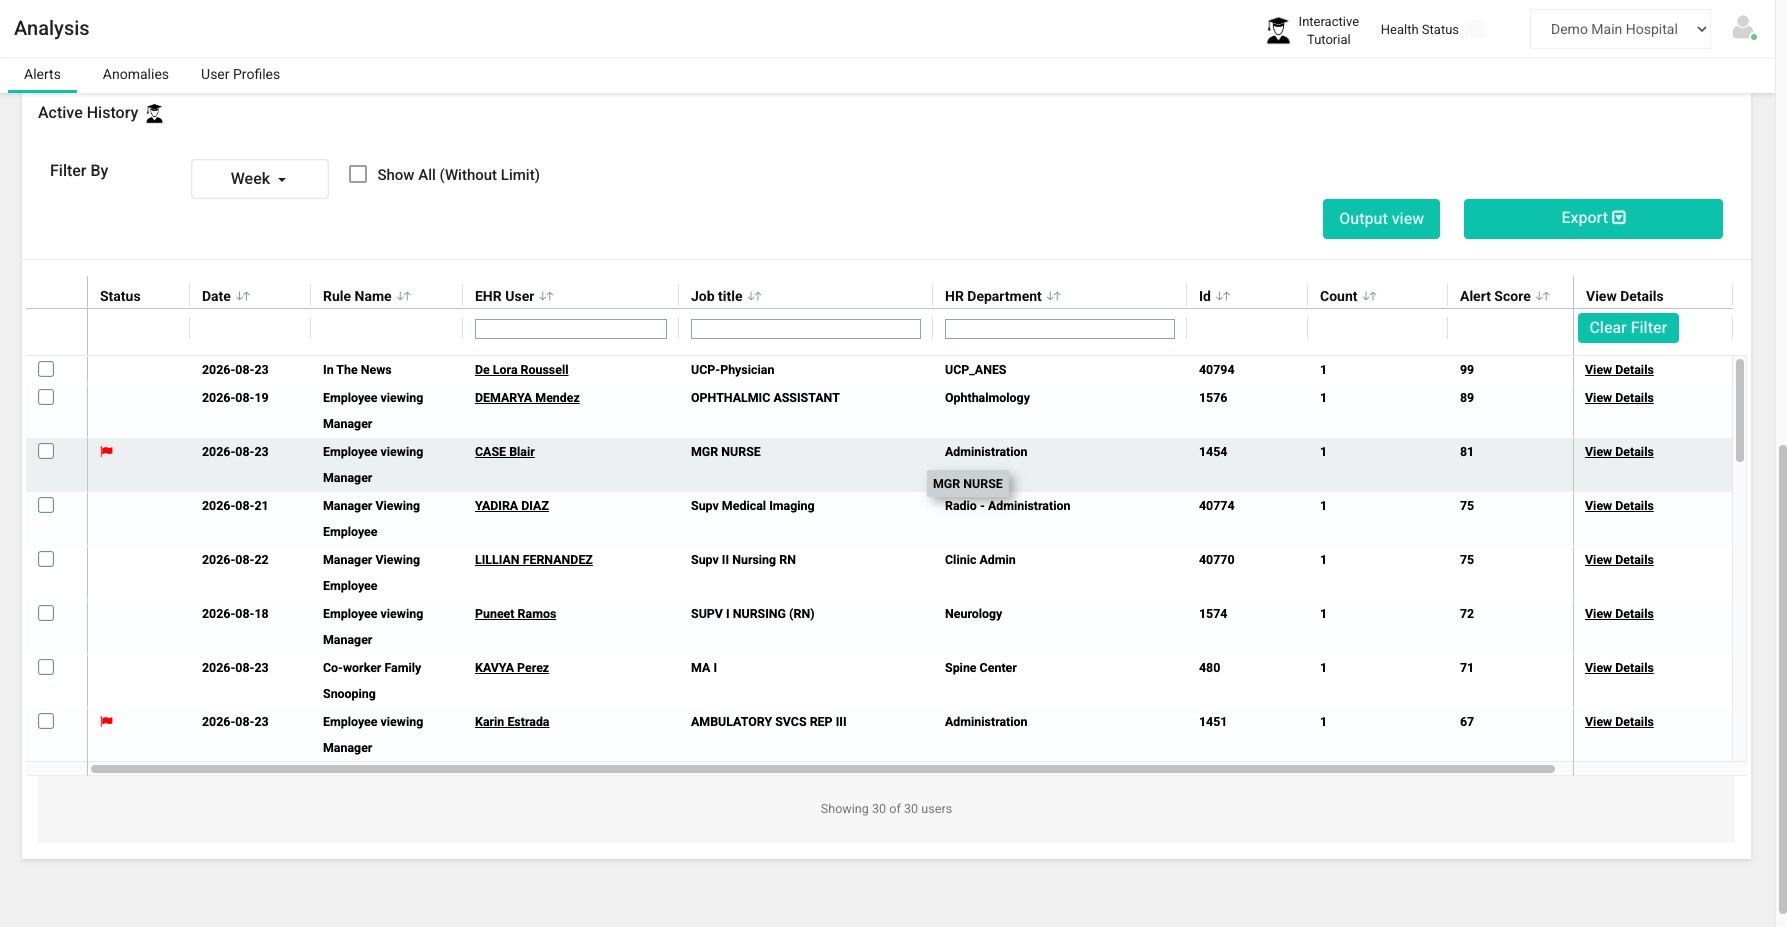
Where alerts become cases and cases become records. When a finding warrants investigation, it converts directly into a structured case with full context already attached. Every subsequent action is logged: notes, evidence, task assignments, decisions.
Compliance Operations
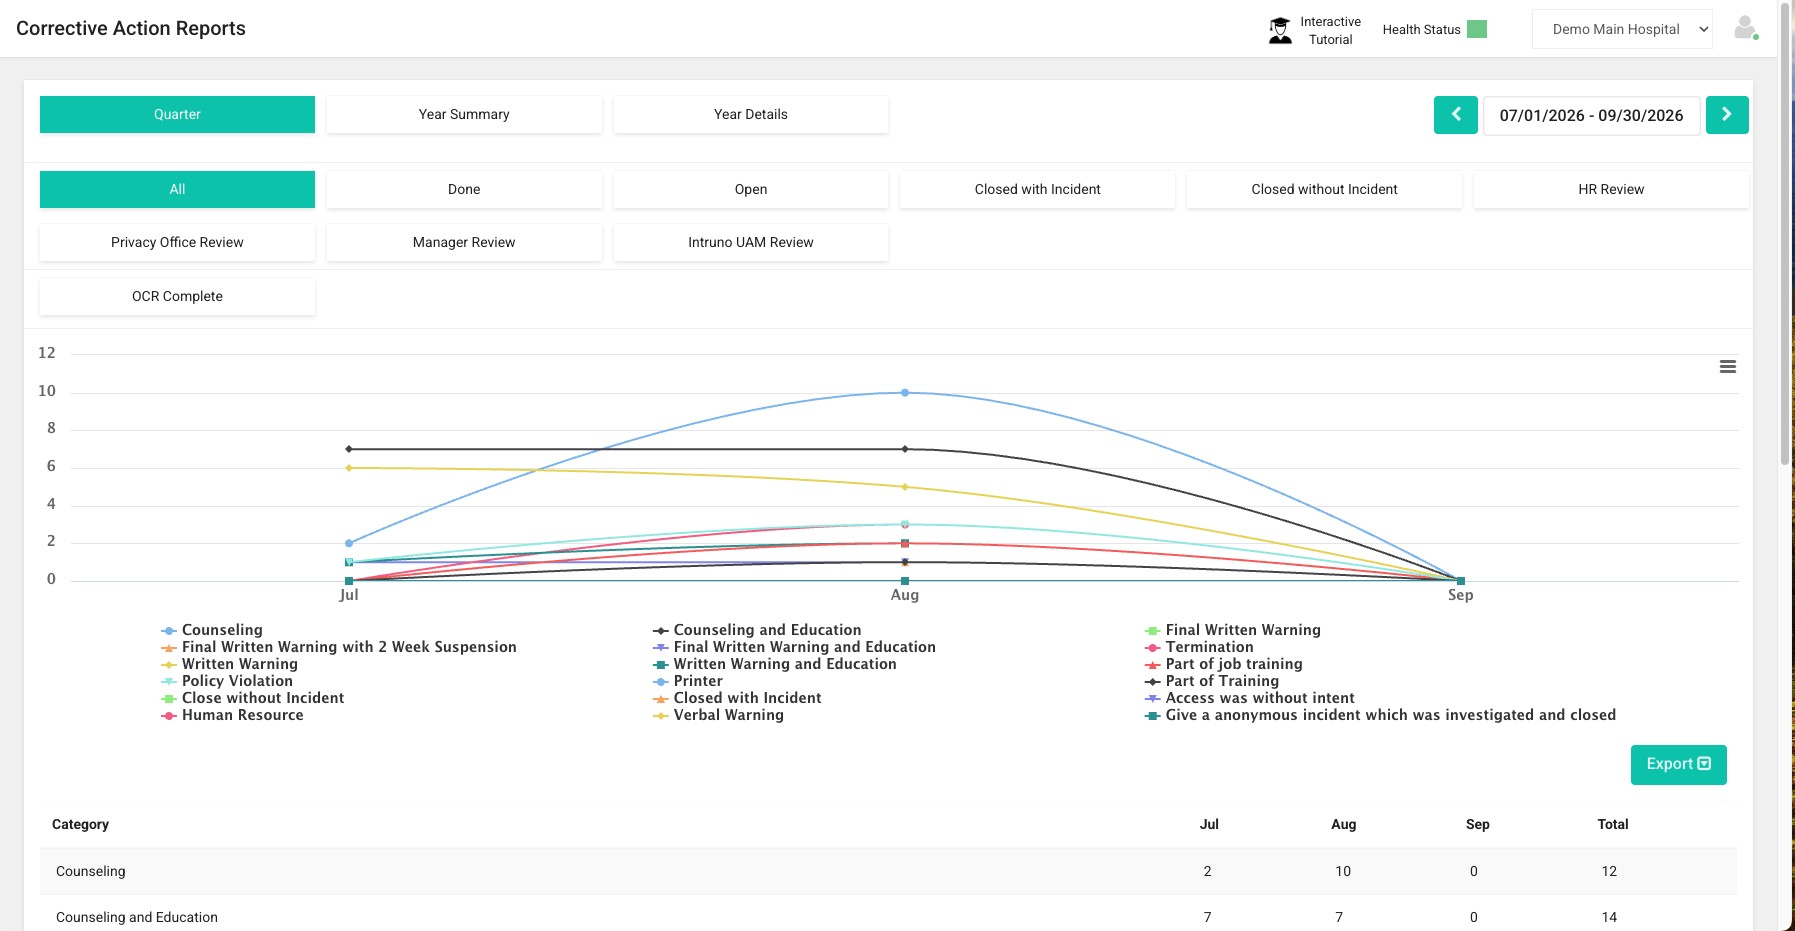
The operational infrastructure layer. Beyond monitoring and investigating, healthcare compliance programs require ongoing program management: continuous corrective action tracking, documentation practices, and OCR readiness. Compliance Operations brings these into the same platform so information flows rather than fragments.
Analytics & Reporting
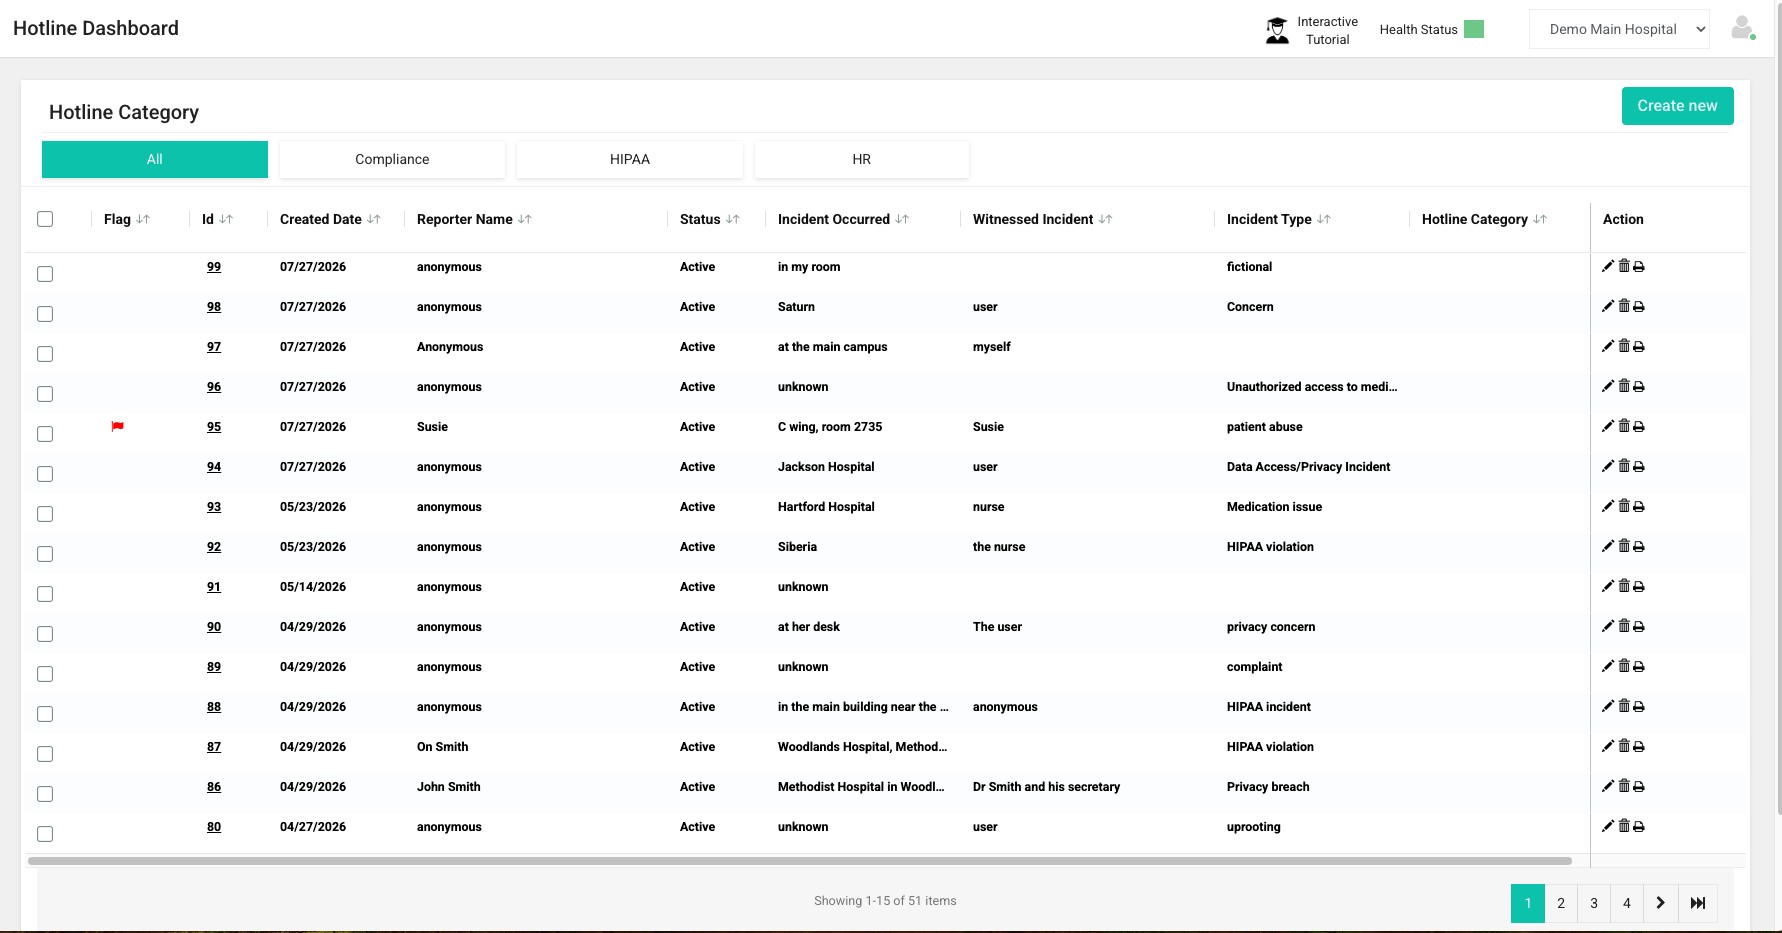
The program-level view. Analytics aggregates data from monitoring, investigation outcomes, and compliance operations to give privacy officers and leadership a clear picture of program performance. Reports generate from real activity, not manual compilation.
How Intruno fits into your existing environment
Every clinical system, identity platform, and GRC tool you’ve already invested in continues to do its job. Intruno adds a privacy operations layer that connects what was previously separate, without requiring replacement of anything in your current stack.
Intruno
Privacy operations layer
Deployment
Managed cloud platform, deployed alongside existing EHR and identity infrastructure with a dedicated implementation specialist.
Security posture
Handles PHI under HIPAA Business Associate Agreement terms, with encryption in transit and at rest on secure cloud architecture.
Certifications
Intruno is ONC certified and holds a SOC 2 Type II report. The SOC 2 report is available under NDA on request.
Scalability
Architected for community hospitals through large integrated delivery networks, scaling with users and access event volume.
Implementation & support
Every implementation includes a dedicated Intruno specialist managing connection, policy configuration, and onboarding.
Procurement
Standard HIPAA Business Associate Agreement. Vendor security questionnaires, BAA review, and integration security documentation available on request.
One platform. Views tailored by role.
Privacy programs involve multiple teams with different jobs. Intruno gives each team what they need from the same underlying platform, without separate tools or manual data transfer between roles.
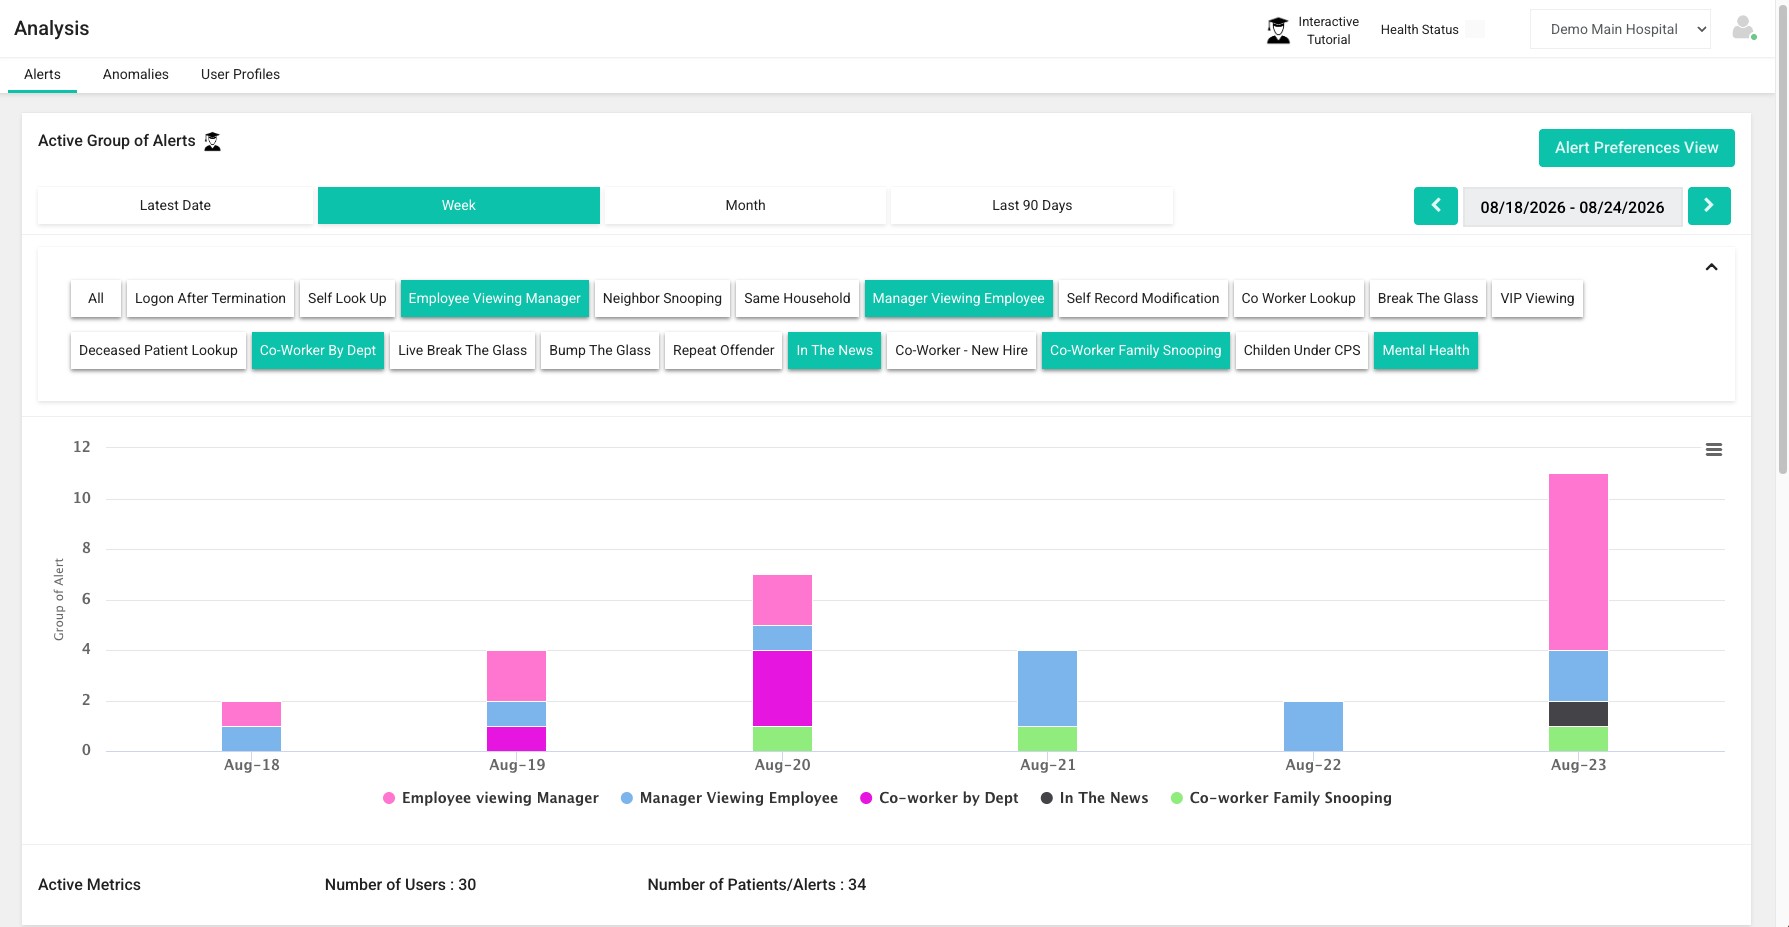
The program dashboard
Program health, open investigations, resolution trends, and compliance status, without asking the team to compile a report manually.
- Reviews program health at a glance
- Approves escalations and high-risk cases
- Accesses on-demand compliance reports
- Tracks metrics for board reporting
The investigation workbench
Alerts arrive with clinical context attached. Cases open in one step. Evidence, notes, and tasks all happen inside the same view.
- Reviews and triages incoming alerts
- Opens and manages investigation cases
- Logs evidence, notes, and correspondence
- Closes cases with documented dispositions
The compliance record
Every monitoring action, investigation step, and case closure builds the audit trail continuously, not retroactively.
- Accesses investigation audit trail
- Manages breach risk assessments
- Exports to GRC platforms
- Generates OCR audit documentation
The workforce access view
Behavioral alerts validated against clinical workflow before they reach the security team, not raw access anomalies requiring manual triage.
- Reviews high-risk behavioral patterns
- Monitors post-termination access attempts
- Tracks shared credential incidents
- Coordinates on escalated security cases
The integration layer
An implementation project with a defined scope, then a stable connected system. Clinical workflows are unaffected. Ongoing maintenance is minimal.
- Manages EHR and identity connections
- Oversees implementation timeline
- Reviews integration health and status
- Manages provisioning and access controls
The governance view
Evidence that a serious privacy program is operating, generated by the program itself, not assembled by staff before a board meeting.
- Accesses board-level summaries
- Reviews program maturity over time
- Supports regulatory inquiry response
- Demonstrates compliance posture